AI-Powered
Managed SOC Operations
NoaSec's AI-Powered SOC pairs machine-learning detection, autonomous alert investigation and automated response playbooks with Tier 1–3 human analysts. AI handles the noise at machine speed; our experts validate, hunt and respond — giving you enterprise-grade 24/7 protection without building an in-house SOC.
What is an
AI-Powered SOC?
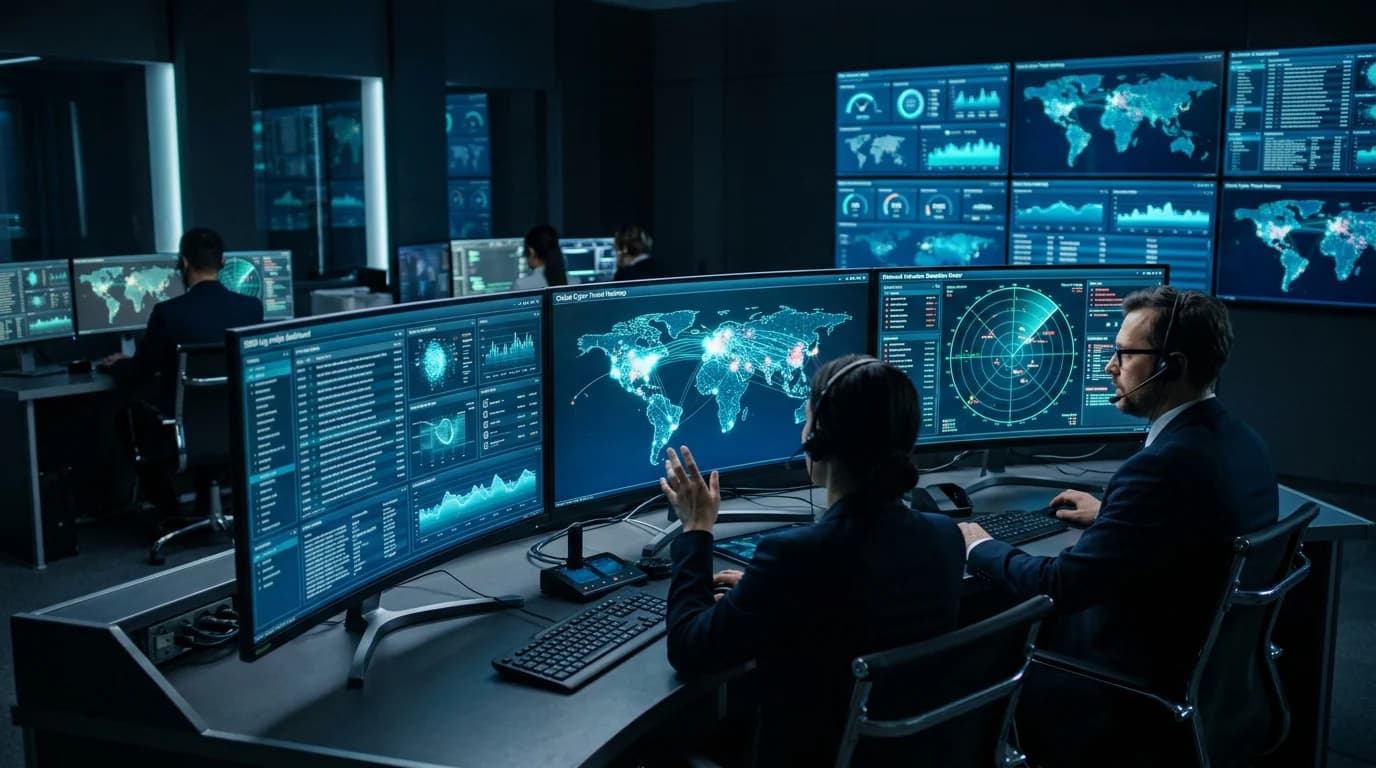
An AI-powered Security Operations Centre uses machine learning, behavioural analytics and automation to detect, investigate and respond to cyber threats at machine speed — with human analysts supervising every critical decision.
Traditional SOCs drown in alerts: analysts spend most of their shift closing false positives while real attacks wait in the queue. NoaSec's AI SOC automates triage, investigation and first response, so our Tier 1 to Tier 3 analysts spend their time where human judgement matters — validating incidents, hunting threats and guiding your team through remediation.
AI SOC Capabilities
Artificial intelligence embedded at every stage of detection and response.
AI Threat Detection & Correlation
Machine-learning models correlate endpoint, network, cloud and identity telemetry, turning thousands of raw events into a handful of high-confidence incidents.
AI-Driven Alert Triage
Every alert is automatically enriched, scored and de-duplicated, so false positives are suppressed before an analyst ever has to look at them.
Autonomous Investigation
AI investigation agents gather context — process trees, user history, threat intel, related hosts — and draft a plain-language incident summary in seconds.
Automated SOAR Playbooks
Pre-approved playbooks isolate endpoints, disable compromised accounts and block malicious IPs or domains automatically, cutting response time from hours to minutes.
UEBA & Anomaly Detection
User and Entity Behaviour Analytics baselines normal activity and flags insider threats, compromised credentials and lateral movement that rules miss.
AI-Assisted Threat Hunting
Analysts use AI to hunt across your data with natural-language queries, mapped to MITRE ATT&CK, uncovering stealthy attackers before they strike.
How Our AI SOC Works
From raw telemetry to contained threat — automated where it is safe, human-led where it matters.
- 01
Ingest
Logs and telemetry from endpoints, firewalls, cloud, M365 and identity flow into the SIEM / XDR.
- 02
AI Correlate
ML models enrich, score and correlate events against threat intelligence and behaviour baselines.
- 03
Auto-Investigate
AI agents gather evidence and build an incident timeline with a recommended action.
- 04
Automated Response
SOAR playbooks contain confirmed threats instantly — isolate, block, disable.
- 05
Human Validation
Tier 1–3 analysts verify, escalate and lead remediation with your team.
- 06
Continuous Learning
Analyst feedback retrains models and tunes detections, so the SOC gets sharper every week.
Traditional SOC vs AI-Powered SOC
Why organisations are moving to AI-driven security operations.
| Capability | Traditional SOC | NoaSec AI-Powered SOC |
|---|---|---|
| Alert handling | Manual review, high false-positive fatigue | AI triage suppresses noise and prioritises real threats |
| Investigation | Analysts gather context by hand | Autonomous investigation drafts the case in seconds |
| Response | Manual containment after escalation | Automated SOAR playbooks act in minutes |
| Unknown threats | Signature and rule based only | Behavioural ML and UEBA catch novel attacks |
| Scalability | More data needs more analysts | AI scales with your data volume |
| Improvement | Periodic manual rule tuning | Continuous learning from analyst feedback |
Why Organizations Choose
AI-Powered SOC
Machine-Speed Detection, Human Judgement
AI watches every event 24/7/365 while experienced analysts validate and lead every critical response — no gaps on weekends, holidays or off-hours.
Drastically Reduced MTTD & MTTR
AI triage, autonomous investigation and automated SOAR playbooks shrink Mean Time to Detect and Mean Time to Respond from hours to minutes.
No More Alert Fatigue
AI suppresses false positives and de-duplicates alerts, so only validated, high-confidence incidents reach you — with audit-ready evidence for CERT-In, ISO 27001 and PCI-DSS.
Significant Cost Efficiency
Automation lets a smaller analyst team cover more data, so you get an enterprise AI SOC without hiring, training and retaining three internal shifts.
Professional SOC Certifications
Equip your staff with accredited, battle-tested defensive security credentials.
AI-Powered SOC FAQs
Clear, transparent answers to help you make informed security and digital growth decisions.
What is an AI-powered SOC?
An AI-powered Security Operations Centre uses machine learning, behavioural analytics and automation to detect, triage, investigate and respond to cyber threats at machine speed, while human analysts validate incidents and lead critical decisions.
Does AI replace human SOC analysts?
No. AI handles high-volume, repetitive work such as alert triage, enrichment and first-response containment. NoaSec's Tier 1–3 analysts validate every critical incident, hunt for advanced threats and guide your remediation.
How does an AI SOC reduce false positives?
AI models enrich each alert with context, correlate related events, compare activity to behavioural baselines and score confidence, so duplicate and benign alerts are suppressed before they reach an analyst.
What is SOAR in an AI SOC?
SOAR (Security Orchestration, Automation and Response) runs pre-approved playbooks — such as isolating an endpoint, disabling a compromised account or blocking a malicious IP — automatically when a threat is confirmed.
Which platforms does the NoaSec AI SOC work with?
We integrate with leading SIEM and XDR platforms including Wazuh, Splunk, Microsoft Sentinel, the ELK stack and Cylerian's AI-native XDR, plus firewalls, Microsoft 365, Google Workspace and AWS/Azure cloud logs.
Does the AI SOC help with CERT-In compliance?
Yes. Continuous monitoring, 180-day log retention support and rapid AI-assisted incident analysis help you meet CERT-In directions, including the 6-hour incident reporting requirement.
Related SOC Ecosystem Services
Combine continuous monitoring with specialized reactive and proactive capabilities.
Ready to upgrade to an AI-powered SOC?
Connect your log sources to our AI-driven, human-validated Security Operations Centre with zero business disruption. Ask for a free SOC readiness assessment.